
11 posts tagged with "events"

CLEARSECLABS events

View All Tags

To the Frontier and Back Again
· 6 min read
clearseclabs
Cyber Security Research & Training

In September I gave a talk at [un]prompted.au in Sydney called To the Frontier and Back Again. The question behind it was simple. What does vulnerability research look like at the frontier right now, and how much of that can I bring back to models I can run myself?

The frontier half is two Windows system-service 0-days, found with Claude Code and Opus 4.8. The first confirmed root cause landed 1 hour, 16 minutes, and 5 seconds after my first request. The back-again half replays the same hunt on open-weight models: same target, same context, same tools.

Thanks to the [un]prompted.au organizers for a really well-run conference. A lot of the program circled the same thing I was there to talk about: agents, local models, and the feedback loops that make them useful.
Lessons Learned Running Two Agentic RE Workshops at DEF CON 34

· 7 min read
clearseclabs
Cyber Security Research & Training

A small model on a laptop found the bug. The system around it is what told the real one from the thirty that looked just as convincing.

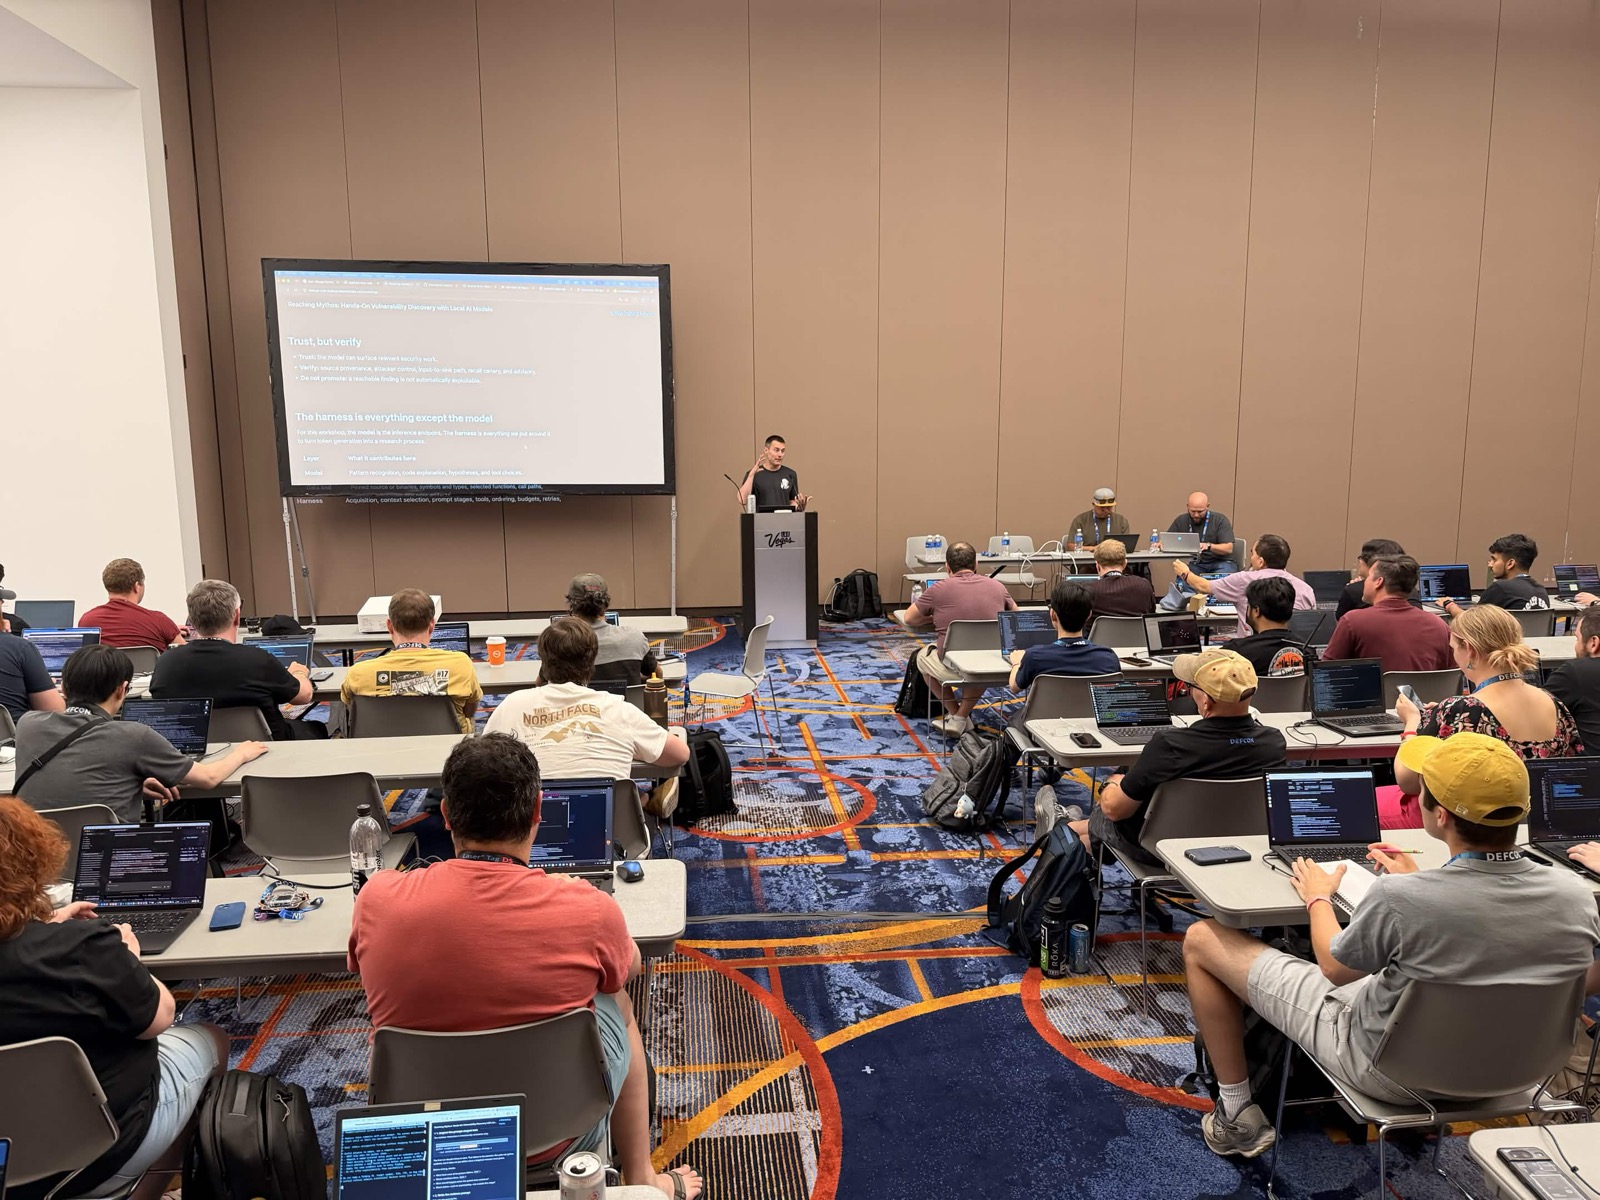
The Reaching Mythos workshop room at DEF CON 34, attendees on laptops with the Trust, but verify slide on the projector
Reaching Mythos, Friday at DEF CON 34. Trust, but verify: the harness is everything except the model.

I taught two four-hour workshops at DEF CON 34, both built around one question: how close can local AI models get to frontier-level reverse engineering, and what do I have to build around them to close the gap?

Both workshops came at that question from opposite ends and landed in the same place. The model is rarely what decides whether you find the bug. What decides it is everything around the model: how you feed it evidence, which tools it can reach, where you make it stop, and whether or not you can validate the result.

Agentic Diffing Apple Security Updates: RE//verse 2026 Talk

· 2 min read
clearseclabs
Cyber Security Research & Training

If you're curious about how AI can accelerate your reverse engineering workflows, check it out. Especially useful if you're looking to get started with agentic RE.


The video is up from our talk at RE//verse 2026 in Orlando, Agentic Diffing Apple Security Updates.

44con - London

· One min read
clearseclabs
Cyber Security Research & Training

Conference speaking and training opportunity at 44CON, a public event bringing together the best in UK and International information security research and networking opportunities and trainer teaching

BlackAlps - Yverdon-les-Bains

· One min read
clearseclabs
Cyber Security Research & Training

"Black Alps conferences are events enabling to discuss the latest threats, mitigations and advances in cyber security. The event features cyber security experts from Switzerland and abroad. It is addressed to anyone with an interest in cybersecurity or connected to the internet, e.g., CEOs, CIOs, CISO, CTOs, developers, and researchers." CSL gave a talk on the main track presenting a slick patch diffing tool ghidriff

Blackhat's SecTor - Toronto

· One min read
clearseclabs
Cyber Security Research & Training

SecTor has built a reputation of bringing together experts from around the world to share their latest research and techniques involving underground threats and corporate defences', provided a chance to present CSL's latest contribution to open source for ghidriff at Blackhat's Arsenal

44con - London

· One min read
clearseclabs
Cyber Security Research & Training

Conference speaking and training opportunity at 44CON, a public event bringing together the best in UK and International information security research and networking opportunities and trainer teaching